Framework-mapped findings
Scanner evidence is linked to CIS, OWASP, NIST CSF, ISO 27001, SOC 2, and HIPAA control themes for clearer reporting.
Compliance mapping for AI-built products.
SecureAI is VemeloAI's system for turning security scanner evidence into clear compliance themes. It helps vibe-coded and AI-orchestrated products show what matters for CIS, OWASP, NIST CSF, ISO 27001, SOC 2, HIPAA, and EU AI Act conversations.
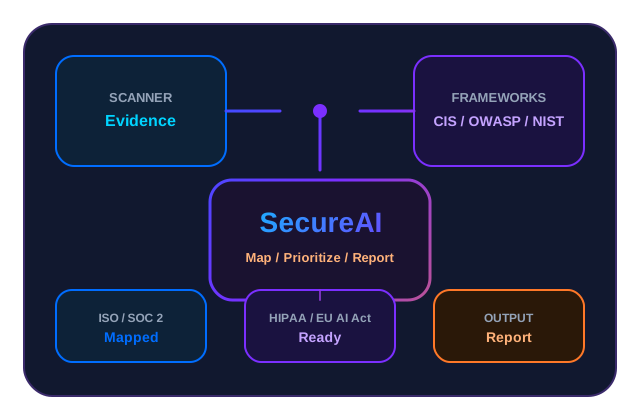
SecureAI is not a certificate. It is a practical mapping and reporting layer that connects technical findings to the frameworks your customers and stakeholders already recognize.
Scanner evidence is linked to CIS, OWASP, NIST CSF, ISO 27001, SOC 2, and HIPAA control themes for clearer reporting.
Teams see where misconfigurations and app risks overlap with compliance-relevant controls, so they fix what matters first.
Talk about security in terms buyers understand: access, encryption, monitoring, hardening, and AI-system risks.
Designed for AI SaaS stacks with apps, APIs, RAG, agents, and infrastructure, not only classic websites.
Use SecureAI outputs as part of broader AI governance discussions around transparency, oversight, logging, and risk.
Combine SecureAI mapping with AI orchestration engineering so delivery speed and compliance stay connected.
Collect evidence from your systems, apps, and infrastructure.
Connect findings to compliance themes across major frameworks.
Focus remediation where risk and compliance impact are highest.
Share clear themes with teams, customers, and stakeholders.
Investors often ask about security certificates and compliance readiness. Here is the clear answer: SecureAI helps you show evidence and a roadmap. Formal certificates come from independent audits when your organization is ready.
Certificates such as ISO 27001 or a SOC 2 Type II report come from independent audits against a defined scope. SecureAI is not a certificate. It maps technical findings to framework themes so teams can prepare evidence, prioritize gaps, and communicate readiness honestly.
SecureAI turns scanner evidence into CIS, OWASP, NIST CSF, ISO 27001, SOC 2, and HIPAA themes for reporting and prioritization. A certificate or attestation is an external opinion that controls are designed and/or operating effectively. You can use SecureAI before, during, and after certification work.
Be precise: explain which frameworks you map to, what evidence you collect, what gaps remain, and what roadmap you follow toward ISO 27001, SOC 2, EU AI Act controls, or other targets. Investors value clarity and progress more than empty claims of being "fully certified."
Common asks include ISO 27001 (ISMS), SOC 2 Type II (control effectiveness), and industry cases such as HIPAA where PHI applies. For AI products, investors also ask about EU AI Act readiness, GDPR, tenant isolation, logging, and vendor risk. SecureAI supports those conversations with mapped themes.
Yes. SecureAI helps organize findings, highlight control themes, and build a remediation path. Certification still requires policies, operating controls, evidence over time, and an independent auditor. We combine SecureAI with AI orchestration and compliance consulting to close that gap.
SecureAI prepares mapped evidence and a clear readiness picture for customers and investors. Formal certificates and attestations (such as ISO 27001 or SOC 2) still come from independent audits. SecureAI does not replace those audits, BAAs, or legal advice.
We can walk through how SecureAI mapping fits your product, customers, investors, and AI regulation goals.